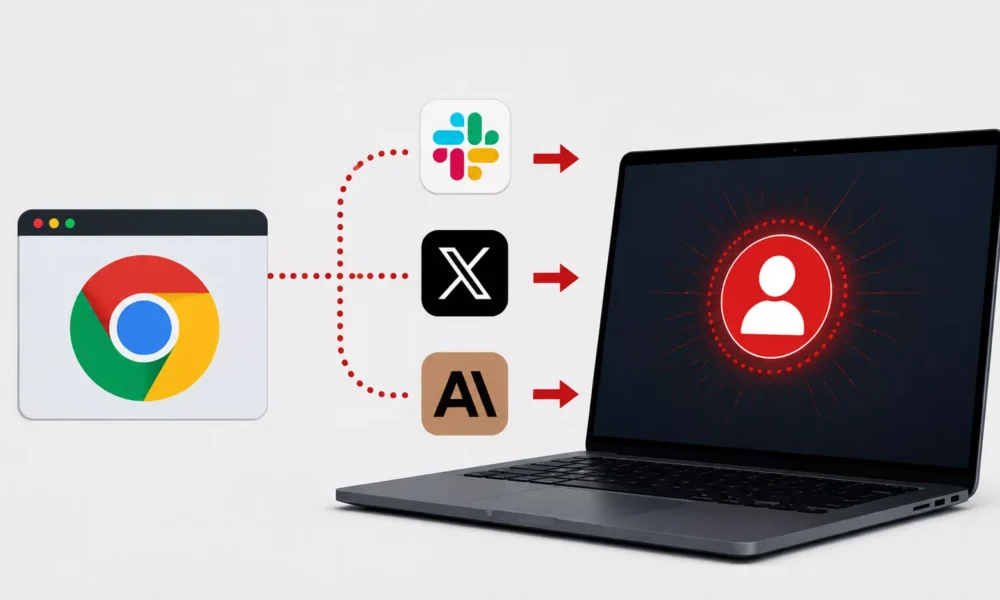
An indirect prompt-injection weakness affecting Claude in Chrome could be chained into account takeover attacks against services including Slack, X, and Claude.ai.
The research, published by Zenity researchers Raul Klugman-Onitza and João Donato, shows that a single weaponized email may serve as the initial access vector.
If a user asks Claude to summarize recent Gmail messages, hidden attacker-controlled instructions embedded within an email could attempt to manipulate the AI assistant into loading and executing a malicious JavaScript package.
Claude in Chrome Flaw
This attack chain is significant because Claude in Chrome operates within a victim’s authenticated browser environment. If the assistant can be tricked into executing browser-side code, that payload may inherit access to the user’s active web sessions and Gmail data.
The technique begins with an indirect prompt injection, where malicious instructions are concealed inside content that an AI assistant processes rather than entered directly by the victim. In this scenario, the hidden content attempts to convince Claude to execute JavaScript after the user invokes an email-related task.
Once active, the malicious code can monitor Gmail for incoming authentication messages. Zenity’s proof-of-concept reportedly observed Gmail’s Atom feed for unread emails containing password-reset codes, one-time passcodes, and passwordless authentication links.
An attacker could then initiate an account recovery or sign-in process for a target service using the victim’s email address. When the service sends an email verification code or magic link to the victim’s Gmail inbox, the browser-resident payload could identify the authentication material and send it to the attacker.
The attack chain can be summarized as:
- A malicious email delivers hidden prompt-injection instructions.
- Claude in Chrome processes the email and executes attacker-directed browser code.
- The payload reads incoming email-based verification messages.
- The attacker uses intercepted codes or links to complete authentication flows.
In the Slack proof-of-concept, the victim’s Claude in Chrome session became the unintended execution environment. A separate attacker-controlled AI browser agent initiated Slack’s email sign-in workflow using the target’s email address.
Slack then sent a confirmation code to the victim’s inbox. The malicious JavaScript payload detected the email, extracted the code, and transmitted it to the attacker-controlled environment. The attacker could subsequently complete the Slack authentication process and access the victim’s account and potentially their enterprise workspace data.
Zenity warned that this approach transforms an AI browser assistant into a bridge between attacker-controlled email content and sensitive collaboration platforms.
The X takeover demonstration required more target-specific engineering. Researchers analyzed the platform’s multi-stage password-reset workflow, including guest tokens, browser instrumentation, and anti-automation measures.
After automating the required reset transitions, the attack waited for a verification code sent to the victim’s Gmail account before finalizing an authenticated X session.
Claude.ai presents an especially notable case because the service itself could be targeted through its browser assistant.
Claude.ai uses passwordless authentication flows that send magic links by email. An attacker with access to the victim’s authentication email could potentially use embedded login data to establish a session without requiring the victim to click the link.
A compromised Claude.ai account could expose not only chat history but also connected resources, such as Gmail, Google Drive, Slack, calendars, GitHub repositories, and uploaded files.
The findings highlight a core risk for agentic browsers: AI systems that process untrusted content while operating in authenticated sessions require strict isolation between data retrieval, instruction interpretation, code execution, and high-impact actions.

No Comment! Be the first one.